AI-Powered Compliance for Canada
From compliance gap to audit-ready — in minutes.
TSL GRC is Canada's only AI-powered governance platform built natively for PIPEDA, OSFI B-10, CIRO, and CCPA. Generate policies, close gaps, and satisfy auditors — automatically.
Trusted by Canadian organizations in financial services, healthcare, and technology
Compliance, operational in minutes
From gap analysis to audit-ready evidence
Canadian compliance is complex. Your current tools weren't built for it.
Spreadsheets & guesswork
Manual gap tracking, version-controlled nightmares, no audit trail.
Months of policy writing
Compliance consultants charge $300/hr. Policies take weeks. Deadlines slip.
Global tools miss Canadian law
US-built GRC platforms don't understand PIPEDA, OSFI, or CIRO specifics.
TSL GRC was built to solve exactly this — for exactly your market.
AI that understands Canadian compliance — end to end.
🍁 Built for Canada
PIPEDA, OSFI, CIRO, CCPA natively integrated. We speak the language of Canadian regulators.
⚡ AI does the work
TSL GRC AI generates, reviews, and flags compliance gaps automatically, saving hundreds of hours.
🔒 Your data, your control
Canadian data residency guaranteed. On-premise AI options available for maximum security.
Built to track Canadian regulations continuously, not just at audit time.
TSL GRC keeps a live map of obligations, controls, evidence, and policy status across major Canadian frameworks. As regulations update, your impacted controls are flagged immediately with prioritized remediation guidance.
Framework Tracking
Native coverage for PIPEDA, OSFI B-10/B-13/B-15/E-21/IS, CIRO, PHIPA, PIPA-AB/BC, Quebec Law 25, and supporting global standards.
Regulatory Monitoring
Continuous ingestion of regulator updates, enforcement actions, and guidance changes with impact scoring and deadline-aware triage.
Execution Discipline
Monitoring features include live regulatory tracking, impact mapping, owner-based alerting, and evidence freshness controls.
View Monitoring Center →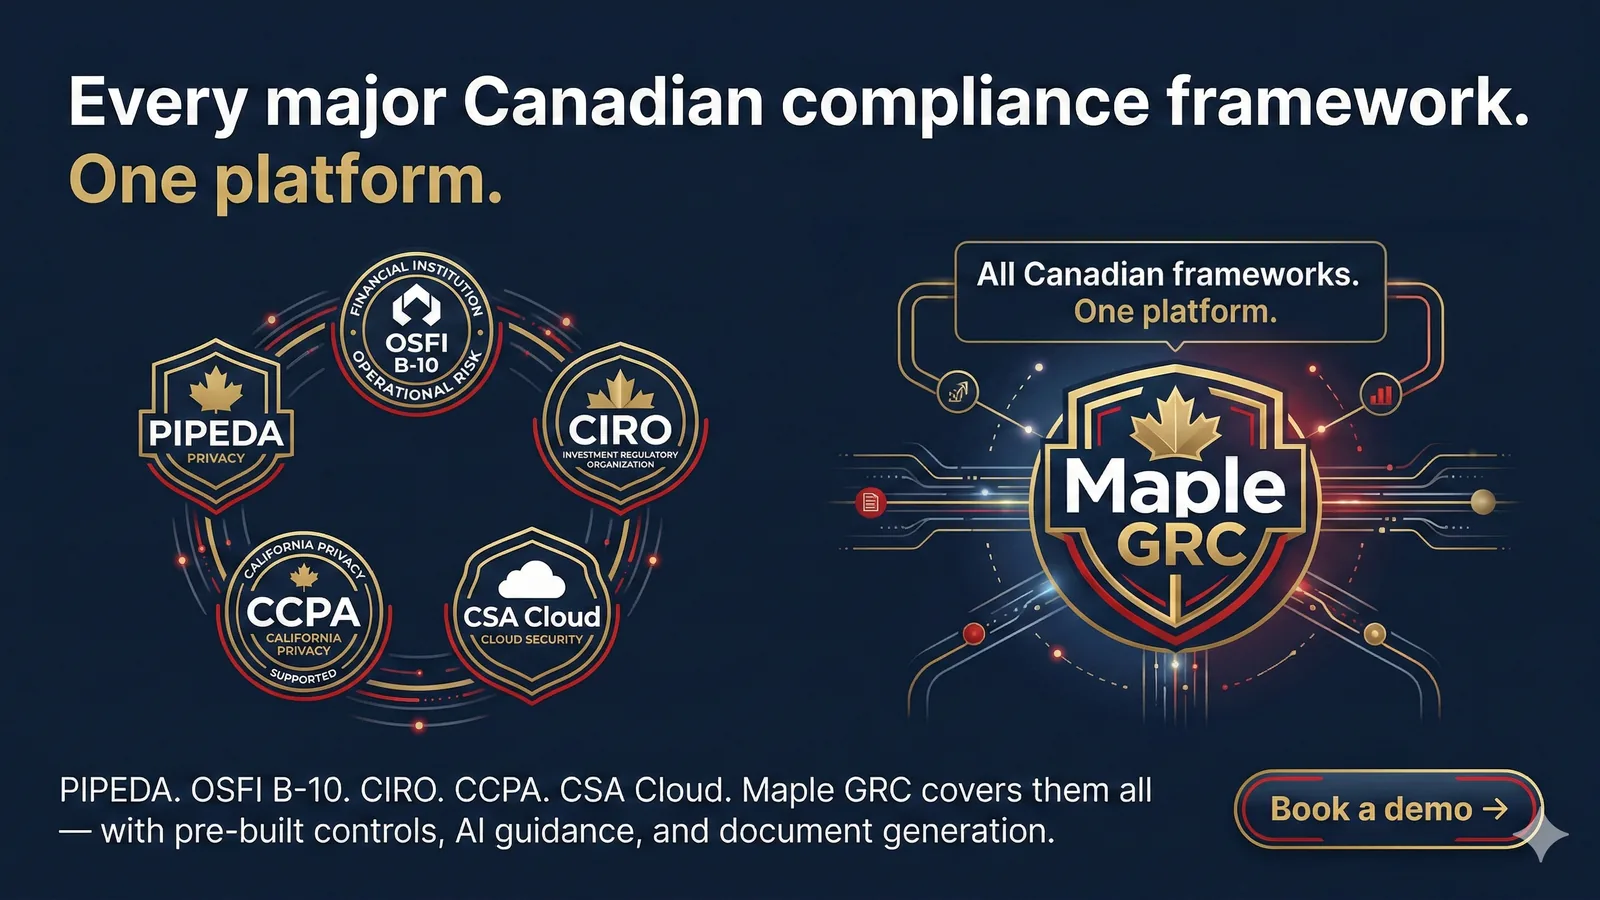
Know every gap. Close every gap.
Run a complete gap analysis across PIPEDA, OSFI, CIRO, and CCPA in minutes. TSL GRC AI maps your current state against 3,222+ controls and prioritizes exactly what needs fixing. Non-compliance is costly — our AI stops fines before they happen.
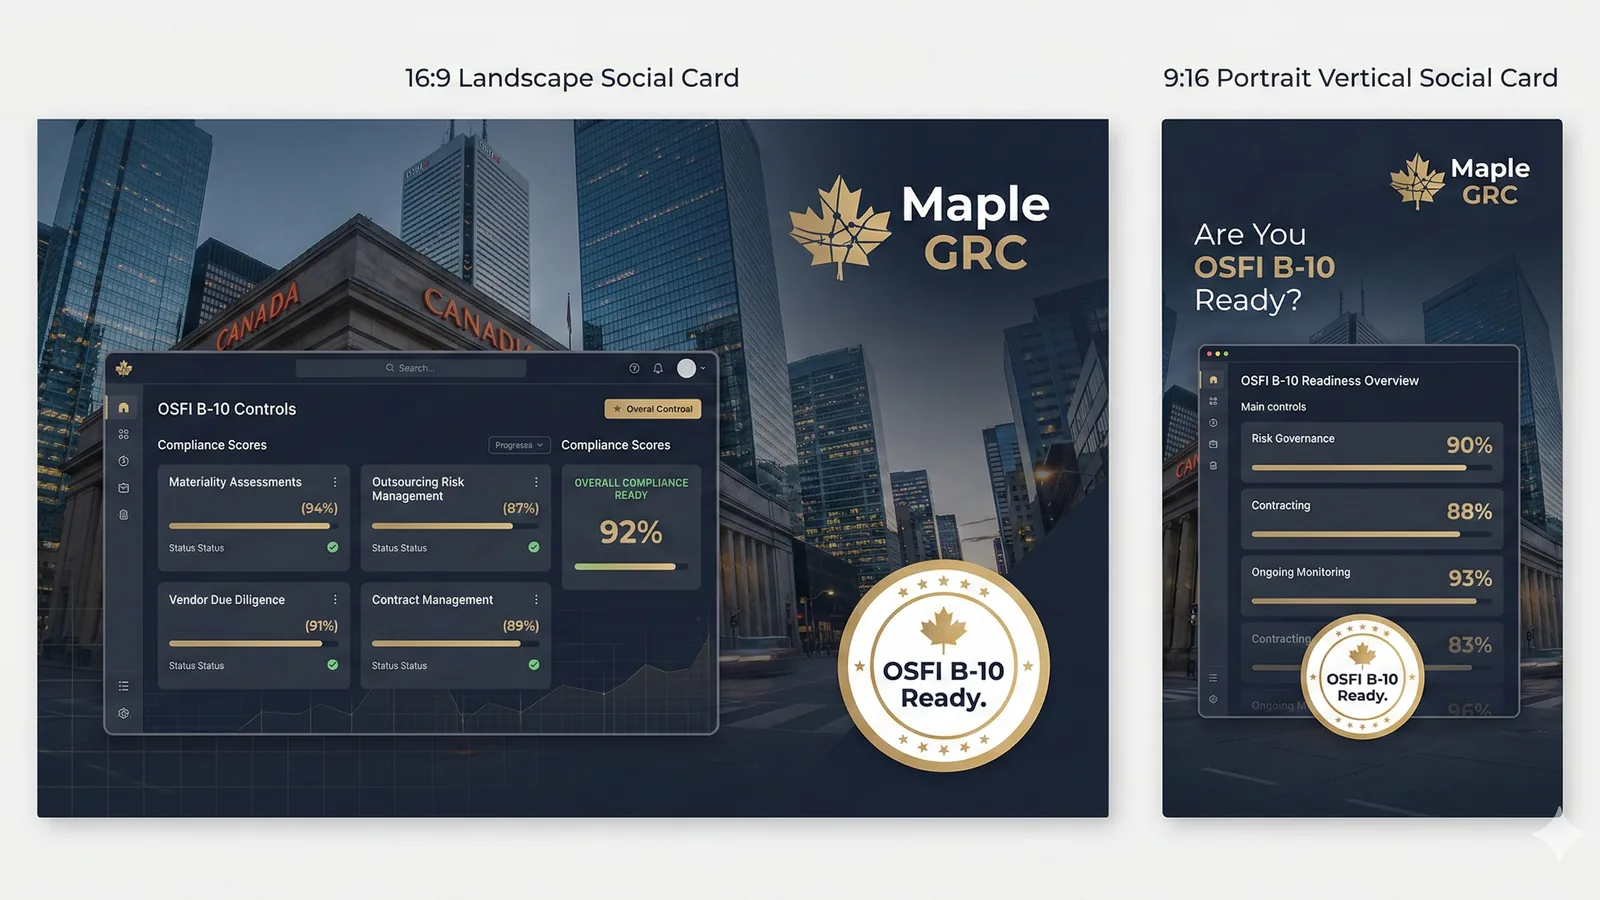
Policies written by AI. Approved by humans.
Stop writing compliance documents from scratch. Without internal policy or structure, everyday tasks elevate organizational risk. TSL GRC AI generates PIPEDA-ready, OSFI-aligned policies, bringing order to chaos.
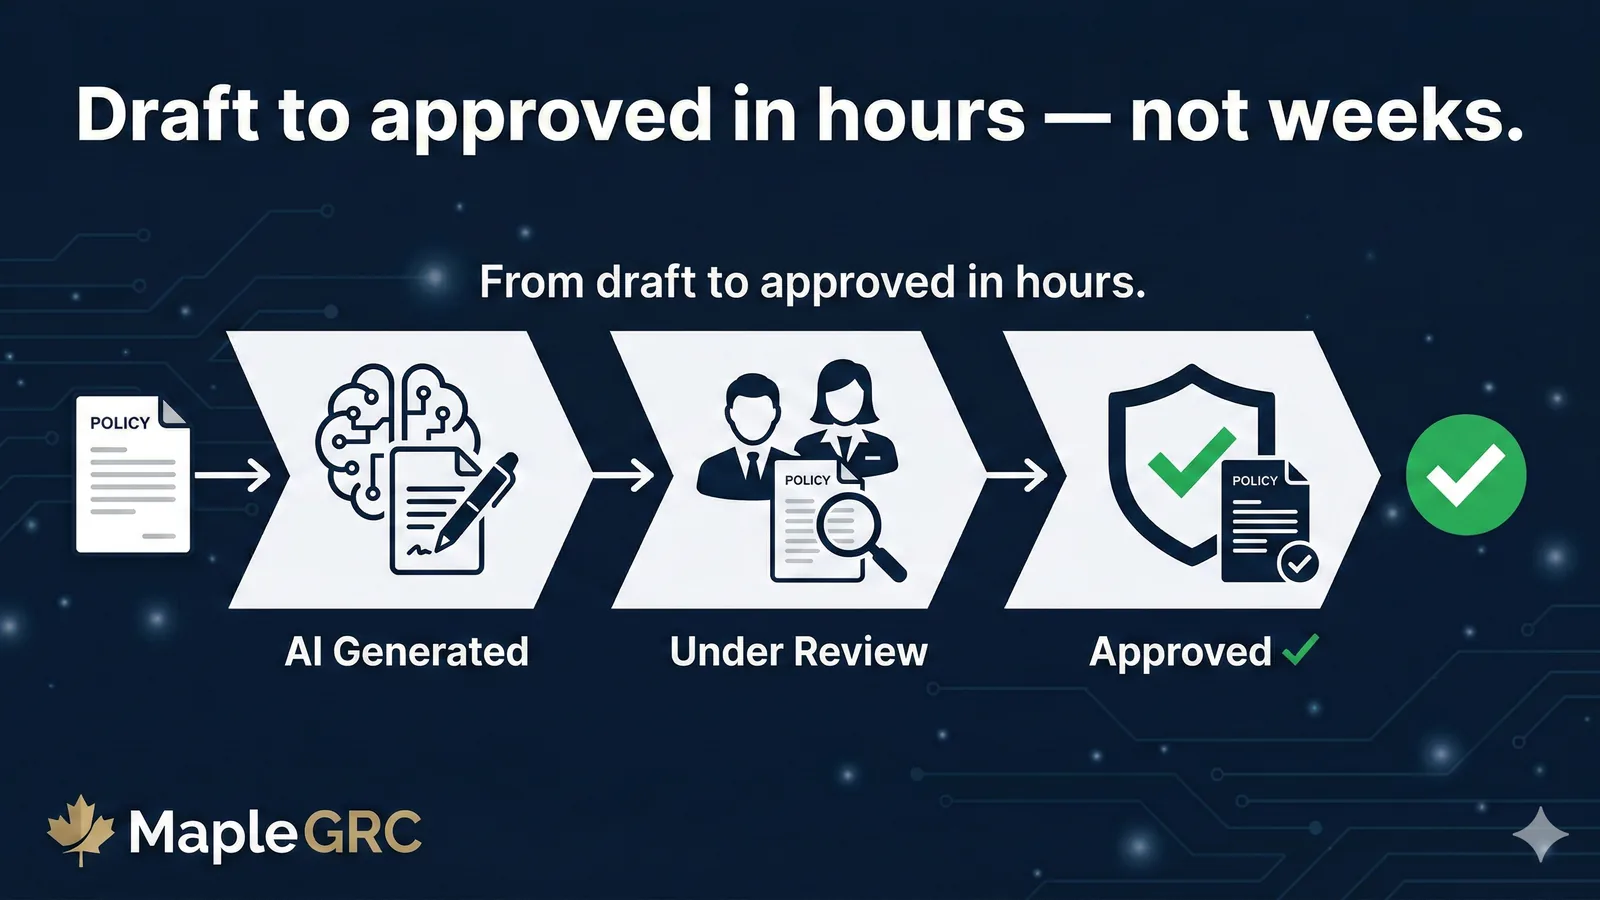
Your compliance register — alive and intelligent.
Every control, every framework, every policy — organized in a living compliance register that updates as your environment changes. Strong governance improves the overall performance of your organization.
Every major Canadian compliance framework — covered.
PIPEDA
Personal Information Protection and Electronic Documents Act
Explore coverage →OSFI B-13
Technology and Cyber Risk Management
Explore coverage →CIRO
Investment Dealer & Partially Consolidated Rules
Explore coverage →PHIPA
Personal Health Information Protection Act (Ontario)
Explore coverage →QC Law 25
Act Respecting the Protection of PI in the Private Sector
Explore coverage →ISO 27001
International standard for ISMS
Explore coverage →“TSL GRC turned a 3-month PIPEDA audit preparation into a 3-day exercise. The AI policy generation is incredibly accurate for Canadian law.”
David Chen
CISO, FinTech North
“Finally, a GRC platform that understands OSFI B-10 out of the box. We didn't have to spend weeks mapping controls manually.”
Sarah Jenkins
VP Risk, Laurentian Credit
“The ROI was immediate. We saved over $40,000 in consulting fees in our first year alone, and our compliance posture has never been stronger.”
Michael Tremblay
CTO, HealthTech Solutions
Sync your cloud infrastructure and identity providers.
On-premises, cloud, or hybrid. TSL GRC integrates with the tools your team already uses.
Accountability, mapped
Compliance org charts, generated for you
TSL GRC turns your people and control assignments into a clear accountability map — who owns which policy, and who signs off. Every unfilled role is flagged, so a governance gap is as visible as a missing control.
- ✓Maps executives (CEO, CISO, DPO, CTO, CFO) to the controls and domains they’re accountable for.
- ✓Generates a per-person Job Description: owned policies, evidence to collect, cadence and a sign-off block.
- ✓Flags missing owners so accountability gaps surface early.
Set it, and it keeps running
Automations that keep evidence fresh
Connect Azure and Google once. TSL GRC discovers assets, collects evidence, runs scans, and maps every finding back to your controls — on a schedule, with a tamper-evident audit trail. Automation is governed as strictly as your people: human owner, grounding, and four-eyes on sensitive actions.
- ✓Scheduled cloud discovery & evidence collection for Azure and Google.
- ✓Findings map straight to controls and update your live score.
- ✓Every automated action is logged, attributable and reviewable.
Canadian data, under Canadian control 🍁
Client and corporate data is hosted, processed and recovered entirely within Canada. No architecture that exposes regulated data to foreign jurisdiction — sovereignty is the default, not an add-on.
Start your compliance journey today.
Free trial. No credit card. Set up in minutes.
Start your compliance program
Tell us what you’re working toward and we’ll spin up your TSL GRC workspace.